Executive summary
One platform for people, workloads and AI agents, on infrastructure and keys you control.
White paper
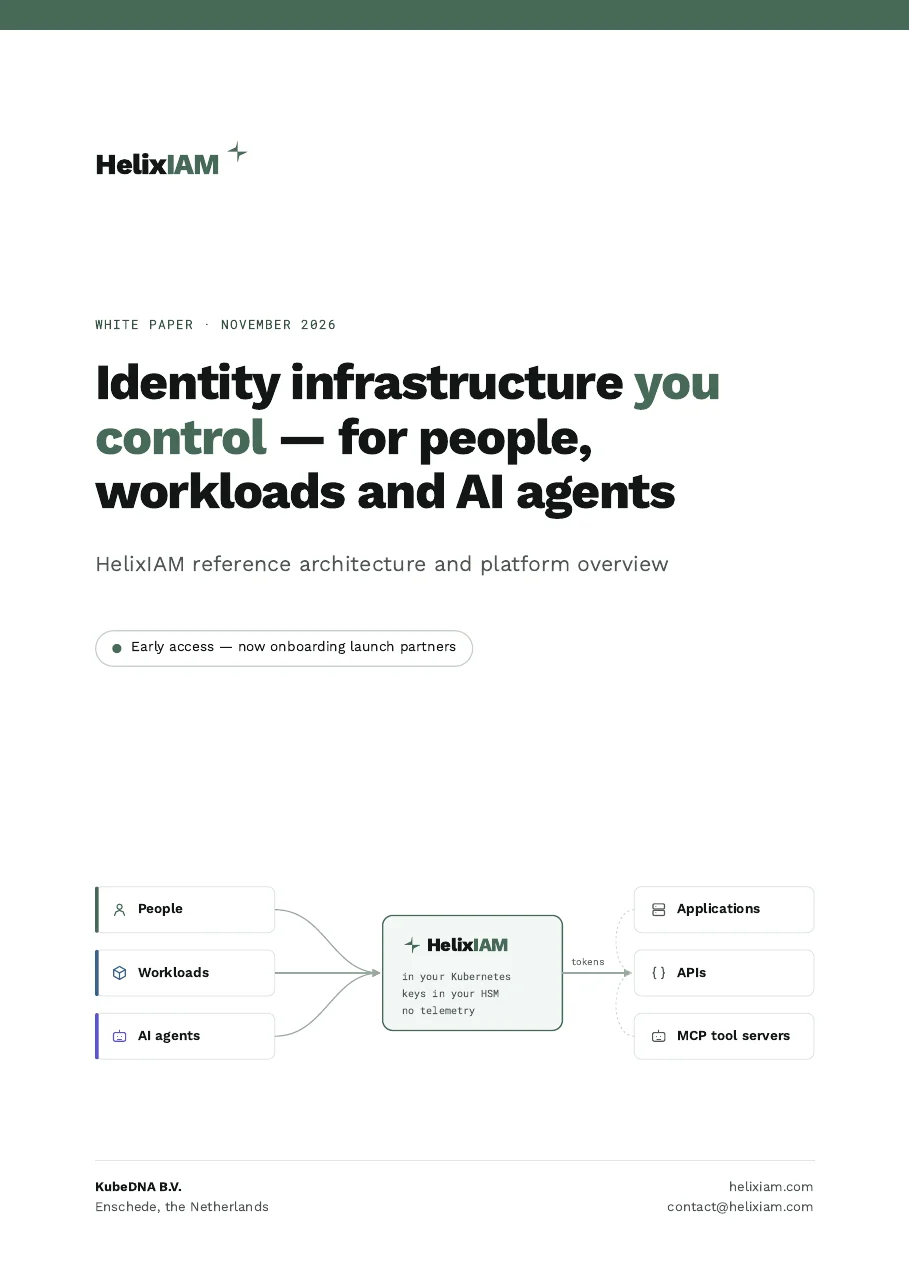
A 12-page overview of HelixIAM for security architects and platform teams: the reference architecture, how agents, workloads and people share one issuer, and where the keys live.
PDF · 12 pages · 1.2 MB · English · describes HelixIAM as of November 2026 · no sign-up needed
What's inside
Read it front to back, or jump to the part your review needs.
One platform for people, workloads and AI agents, on infrastructure and keys you control.
One request can cross a person, an AI agent and several workloads. The questions a security review asks.
Two propositions, HelixIAM AI Identity and HelixIAM Sovereign, on one identity core.
HelixIAM in your own Kubernetes cluster, with a walkthrough of each component and deployment notes.
Owners, lifecycle and suspension, and delegation with RFC 8693 where authority only narrows.
Three custody profiles per realm, HSM and Vault or OpenBao backends, and what happens when a backend is unavailable.
Sign-in, federation and SSO, keyless workload identity, European eID and moving from your current IAM.
Standards, security testing in CI, signed releases with an SBOM, and audit and privacy tooling.
How KubeDNA supports a deployment, and the path from technical demo to pilot.
In a technical demo our engineers show the flows from the paper on a live system and map them to your environment.
With your consent we use Google Analytics to count, in aggregate, which pages are visited. It sets cookies and sends usage data to Google. Nothing loads unless you accept; change your choice any time via Cookie settings in the footer. Privacy policy